AI-ready infrastructure
 Refer and earn


 Ethereum
 Hyperliquid
 Solana
 Arbitrum
 BNB Smart Chain
 Base
 Polygon
 TRON
 Sui
 Robinhood


Incident report: what happened and what customers need to do
Chainstack is committed to the security of our platform and the protection of our customers’ data. In keeping with that commitment to transparency, we are sharing the details of a recent security incident.
What happened
Our findings indicate that this incident was part of a broader AI-powered attack campaign reported in late October. That does not change our responsibility for what happened in our environment.
An external attacker gained unauthorized access to part of Chainstack’s infrastructure through a third-party component. We detected the intrusion, cut the access paths and are hardening our systems.
Customer-facing services continued to operate normally throughout the incident. Customer nodes, the console, and the API were not modified. We do not store payment method details, such as full card numbers or security codes, so they were not exposed.
What was exposed
The attacker accessed a database containing customer account information. Information that may have been exposed includes organization names, account holder names, the email addresses of your organization’s members on Chainstack, and password hashes.
The attacker also had access to systems holding node credentials. We have no evidence they were read, but we are treating them as exposed and ask customers to rotate them.
Timeline
- October 26, 2026: The attacker gained access to a development environment
- October 29, 2026: The attacker gained access to some parts of our production environment
- October 31, 2026: We detected the intrusion and cut the access paths the same day
- November 2, 2026: We finalized the investigation and closed the incident
What we ask customers to do
We are notifying all customers by email and asking them to:
- Change the passwords, including on any other services where they reused the same password.
- Rotate the node credentials. Self-service rotation is now available in the console. Current endpoints keep working until customers complete the rotation, allowing them to rotate credentials without downtime. See the documentation.
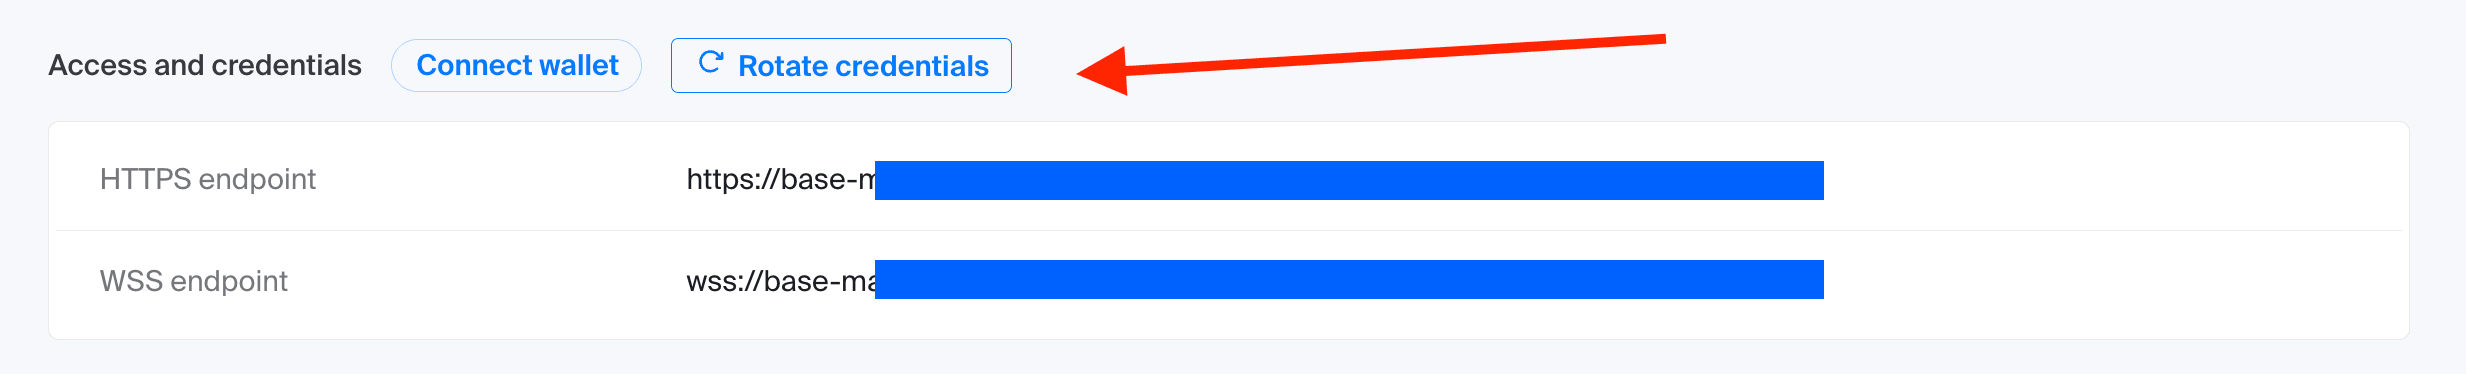
- Regenerate the platform API keys if they use the platform API.
- Watch for phishing messages. Chainstack will never ask for passwords, tokens or keys.
This page is the single source of truth for the incident. We will update it if new information becomes available.
If you have any further questions, contact us.